In short
If your database is reachable from the whole internet, it will be found by bots within hours. Good network design keeps sensitive things off the street and lets only the right traffic in.
Applying security principles specifically to network design — segmenting sensitive systems, minimizing exposed surface area, and defaulting to deny rather than allow, building on Phase 3's networking fundamentals.
Think of it like this
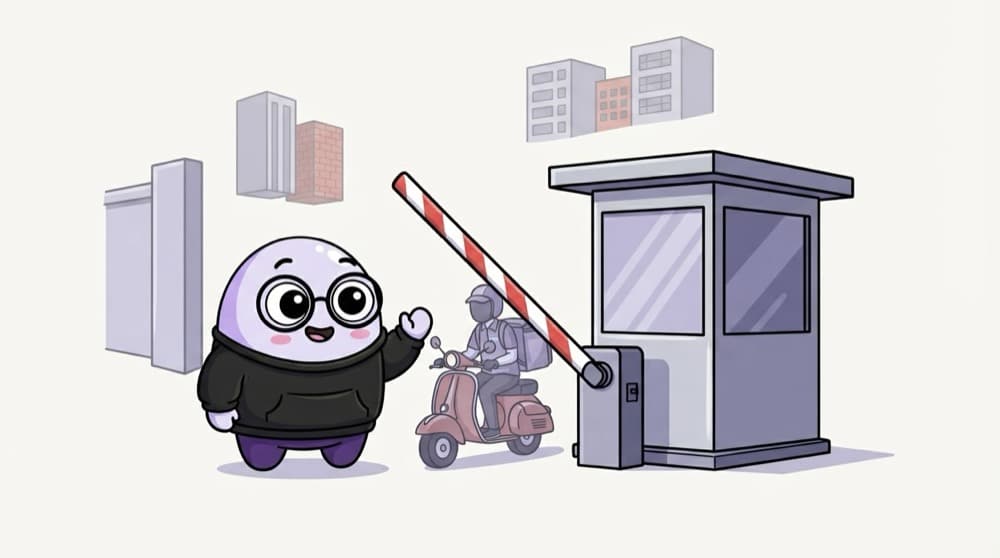
The housing society gate
A gated society has one main gate with a guard. Delivery boys reach the gate, not your bedroom. The clubhouse is open to residents, the water tank room is locked to everyone except the plumber. Networks work the same way: one entry, separate zones, locked by default.
Watch it happen
A typical cloud network layout
1/4Only the load balancer has a public address. It accepts ports 80 and 443 and nothing else.
The big ideas
What you need to know
Default deny
Start with everything blocked, then allow only the ports and sources you need. Not the other way round.
Segment the network
Put web, app and data in separate subnets with rules between them. An attacker in one zone can't stroll into the next.
Shrink what's exposed
Every open port is a door someone will try. Close what you don't use and keep admin ports off the internet.
Encrypt in transit
Use TLS even inside your network. Anyone who sneaks in shouldn't be able to read traffic between services.
See it in code
Walk through the code
1# Which ports is this Linux box listening on?2sudo ss -tulpn3 4# Allow only SSH from the office VPN range and HTTPS from anywhere (ufw)5sudo ufw default deny incoming6sudo ufw allow from 10.8.0.0/24 to any port 22 proto tcp7sudo ufw allow 443/tcp8sudo ufw enable9 10# From another machine you own: what does the outside world see?11nmap -Pn your-server-ip1/3ss lists listening sockets and the process behind each. Anything surprising here is a door you didn't know about.
Only scan machines you own or have written permission to test. Running nmap against other people's servers can break rules and laws.
Save yourself the pain
Common mistakes
Oops
Opening port 22 or 5432 to 0.0.0.0/0 "just for testing".
Do this instead
Allow only your own IP or VPN range. Bots scan the whole internet for open SSH and database ports constantly.
Oops
Trusting anything that is "inside the VPC".
Do this instead
Add rules between tiers too. If one app server is compromised, it shouldn't be able to reach every other system.
Your mission
Lock down a practice VM
Quick check
Where should a production database usually live?
Go deeper
- 1Review a hypothetical network architecture and identify unnecessarily exposed services.
- 2Learn the concept of network segmentation and why it limits how far an attacker can move laterally.
- 3Practice applying a 'deny by default, allow explicitly' mindset to a security group configuration.
More topics at this stop
 DevSecOps Principles ('Shift Left')
 Secrets Management (Vault, AWS Secrets Manager)
 Container & Image Scanning
 IAM & Least Privilege
 Compliance Basics (SOC 2, ISO 27001 Overview)
 Vulnerability Scanning in CI/CD
 Security Incident Response
 Zero Trust Architecture (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
